Insights
from the front lines of offensive security
 14
Customer Perspective: Testimonial from Bochum University of Applied Sciences
Bochum University of Applied Sciences is a university specialising in the forward-looking subjects of technology, economics and health. It combines interdisciplinary courses with social relevance and a deep-rooted awareness of sustainable action. With its two locations in Bochum – the Central Campus and the Health Campus – and the Velbert/Heiligenhaus campus, the university is closely linked to the regional economy and the health sector. International partnerships complement this network and broaden the perspectives for students and researchers.
> continue reading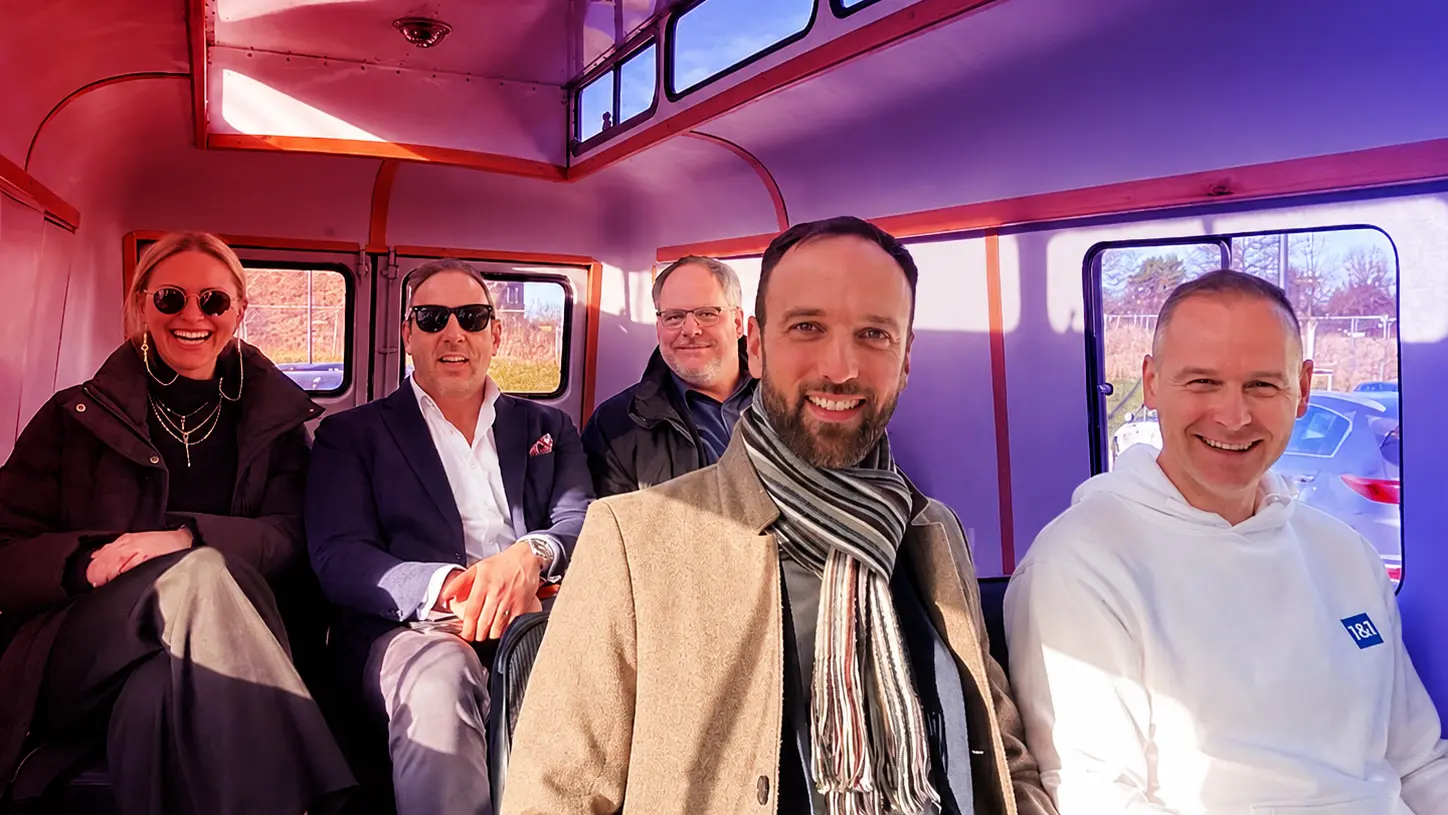 15
Innovation from the Region: Partnerships as Drivers of Sustainable Value Creation
Innovation thrives where knowledge, experience, and diverse perspectives come together. That is why ENTRYZERO brought together representatives from academia, industry, and education to discuss how strong partnerships can drive innovation and create sustainable value. The Event and Its Purpose The event focused on one key question: How can collaboration be leveraged to strengthen unique capabilities, unlock innovation potential, and generate lasting value for everyone involved? One thing became clear: the challenges of digital transformation are best addressed through strong, collaborative networks.
> continue reading 16
Customer Perspective: Testimonial from Bochum Economic Development
“The Bochum Economic Development (BoWE) is one of the largest economic development organizations in Germany. With around 250 employees, it supports businesses & Startups, promotes sustainable urban development, markets and develops properties, and operates technology and startup centers, as well as Bochum’s parking facilities. With over 40 professorial chairs, 1000 students in the field of cybersecurity, leading research at the Horst Görtz Institute for IT Security and the Max Planck Institute for Security and Privacy, Bochum offers a unique environment.
> continue reading 17
Could the Alliance breach have been avoided?
Could the Alliance breach have been avoided? Quick answer: Yes. Another cyberattack on the Allianz Group: After the incident at its U.S. subsidiary Allianz Life, in which data from 1.5 million customers was compromised, a British subsidiary has now also been affected. What happened The ransomware group Clop is currently exploiting the Oracle security vulnerability (CVE-2025-61882) for large-scale cyberattacks. Victims so far include, among others, The Washington Post and a subsidiary of American Airlines.
> continue reading- 18
Could Hertz have been warned months earlier with a better supplier risk management?
Could Hertz have been warned months earlier with a better supplier risk management? Quick answer: Yes. Over 60 organizations were impacted through a single supplier breach at Cleo, exposing data from more than 3,000 Hertz customers alone. The Hertz Corporation was not informed until February 10, 2025, months after the vulnerability was exploitable (source). What happened The Clop ransomware gang exploited a vulnerability (CVE-2024-50623) in Cleo’s managed file transfer software. One vulnerability in a supplier’s system (Cleo) that severely impacted dozens of organizations, including Hertz.
> continue reading - 19
Could the Jaguar Land Rover breach have been avoided?
Could the Jaguar Land Rover breach have been avoided? Quick answer: Yes. According to several sources, Jaguar Land Rover is losing around £72 million in daily sales and £5 million in profit due to the breach. That’s a nightmare for any company. What happened Jaguar Land Rover were hit by a cyberattack in early September. Threat actors exploited a known vulnerability (CVE-2025-31324) in SAP NetWeaver. ENTRYZERO had already identified this CVE as critical back in April, warning that any organization affected should act immediately.
> continue reading  20
Top 5 Vulnerabilities Now on the IT Security Marketplace
Vulnerabilities that are not patched quickly enough are the main reason for most successful attacks, such as ransomware. The question is, which of the many new vulnerabilities are the most relevant? Focus Pays Off With the weekly published Top 5 vulnerabilities most commonly exploited by hackers, the IT Security Marketplace provides organizations with crucial information on where quick remediation action is needed. Transparent AI Model A novel, decision tree-based prioritization approach has been developed, enabling organizations to allocate their resources effectively by focusing on the riskiest vulnerabilities to optimally protect themselves against current threats.
> continue reading 21
Customer Perspective: Testimonial from thyssenkrupp
“As an internationally operating company with a complex IT infrastructure and numerous subsidiaries worldwide, we at thyssenkrupp Materials Services place high demands on our IT security. Conditions As part of a targeted Proof of Concept (PoC), we evaluated the ENTRYZERO platform to gain additional strategic insights for strengthening our cyber resilience, particularly with regard to our decentralized assets. Impact ENTRYZERO impressed during the PoC with its high level of visibility and its ability to assess security from the perspective of potential attackers.
> continue reading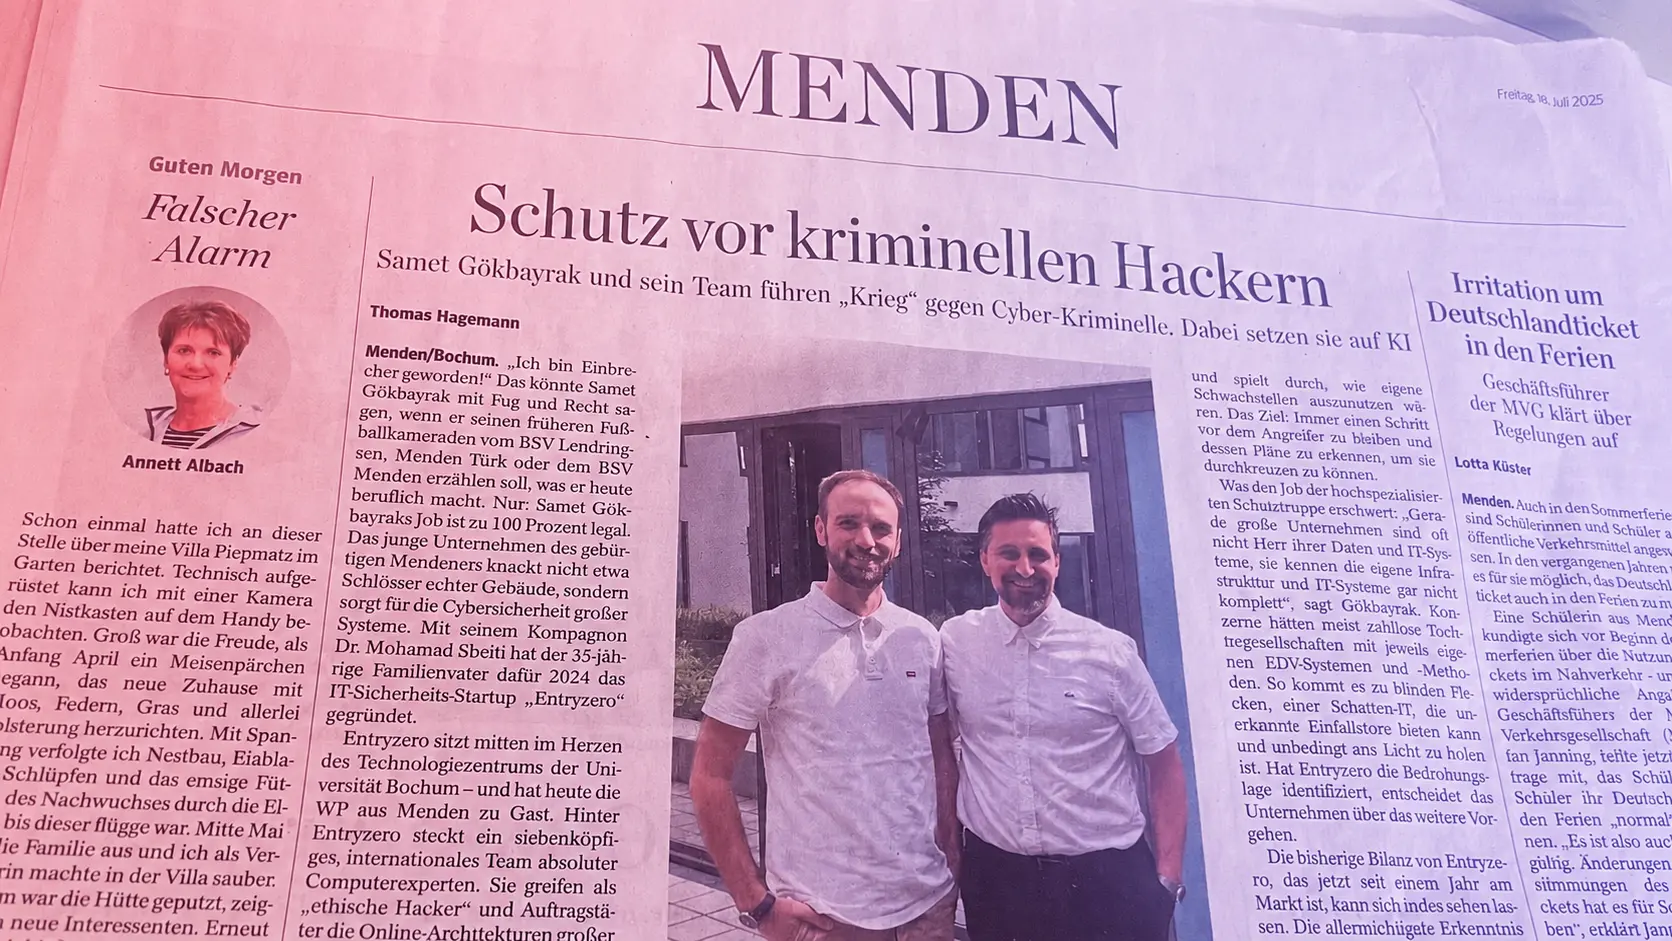 22
ENTRYZERO in the Press: Westfalenpost Reports on Our Mission to Improve Cybersecurity
ENTRYZERO is delighted with the coverage by the Westfalenpost, which offered a behind the scenes look and introduced our mission. The story of our company is told with the opening words, “I became a burglar” from its founding by Samet Gökbayrak and Dr. Mohamad Sbeiti to our daily work in the fight against cyberattacks. Ethical Hacking Meets Artificial Intelligence The Westfalenpost vividly describes how our international team of cybersecurity experts works as so-called “ethical hackers”.
> continue reading- 23
NIST Likely Exploited Vulnerability Model - Helpful, But Not a Game Changer!
This article examines NIST’s new Likely Exploited Vulnerability (LEV) and LEV2 models, which estimate the probability that a vulnerability has already been exploited, complementing existing models and data sources, such as EPSS and CISA KEV. While promising, LEV and LEV2 are not a panacea and require further empirical assessment. Blind Spots - We All Have Them IT security professionals are often faced with a seemingly impossible task: knowing your infrastructure down to the last detail, tracking everything, patching everything, and consequently burning out your operations team, or trying to prioritize what needs to be patched first.
> continue reading  24
IDEA 2025: ENTRYZERO wins at the WORLDFACTORY Demo Day
At the WORLDFACTORY Demo Day awards ceremony, ENTRYZERO was able to celebrate a special milestone at IDEA 2025. The award honors innovative technologies with significant economic potential and confirms our ambition to rethink cybersecurity. At the same time, ENTRYZERO not only made it into the top 3 of participants, securing its place as one of the best spin-offs of Ruhr University Bochum, but also became the only company among all participants to win a place in the STEP USA University Program in New York.
> continue reading 25
MITRE CVE Program: A Single Point of Failure for Global Cybersecurity
The Common Vulnerabilities and Exposures (CVE) program has played a central role in global cybersecurity, providing a unified language for communicating vulnerabilities across researchers, vendors, and defenders. Managed primarily by the MITRE Corporation, with funding from the U.S. government, the CVE system facilitates the timely dissemination of critical cybersecurity information. However, recent developments highlight challenges within its current structure, suggesting strategic improvements are needed. In this article, we look at the process from the discovery and initial reporting to the eventual publication of a vulnerability as a CVE entry.
> continue reading